 Vietnamnet.vn

 Podcast


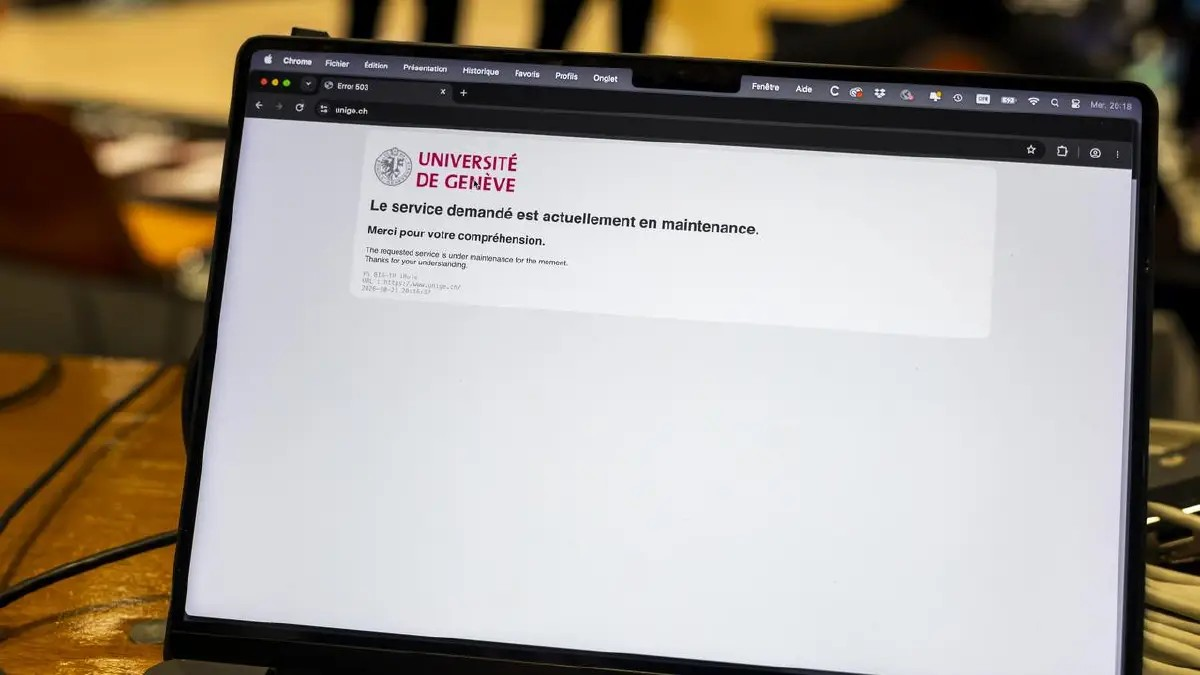
Multiple government websites around the world went offline on October 21 after artificial intelligence systems identified critical security vulnerabilities affecting the PHP programming language, according to media reports.
The risks were considered so severe that the US National Security Agency (NSA) advised organizations using PHP to update their systems immediately or take them offline until appropriate fixes could be implemented.
The US Federal Bureau of Investigation (FBI) also warned that hackers could exploit the vulnerabilities to execute malicious code remotely, potentially compromising sensitive data and network security.
Cybersecurity authorities in Singapore, the United Kingdom, Australia, Canada and the European Union issued similar warnings, highlighting concerns about the potential impact on businesses, government agencies and other organizations relying on PHP-based systems.
Amazon said its threat intelligence team had detected attempts to exploit the vulnerabilities before they were publicly disclosed.
The suspicious activity was identified through MadPot, Amazon's threat detection system designed to monitor potentially malicious activity targeting internet-facing infrastructure.
According to Amazon, the findings suggest that attackers may have attempted to exploit the vulnerabilities before their public disclosure.
However, the company has not determined how the attackers obtained information about the security flaws in advance.
AI plays a growing role in discovering critical vulnerabilities
Meanwhile, Google and OpenAI have emphasized the expanding role of artificial intelligence in identifying and addressing cybersecurity threats.
Google said cybersecurity company Wiz had used AI models to assist in discovering and investigating the vulnerabilities.
Google's Gemini AI tools also helped assess their severity, test potential attack methods and verify security patches.
OpenAI said researchers using its AI models had also contributed to the discovery of critical PHP vulnerabilities.
According to OpenAI, the company has spent the past two months leading a coalition of software developers, cybersecurity researchers and security service providers to coordinate fixes and prepare protective measures before the vulnerabilities became widely known.
The ChatGPT developer described the incident as one of the most significant software security issues in recent times.
The developments demonstrate how advanced AI systems can help uncover weaknesses in widely used software.
However, they also raise concerns that cybercriminals could use similar capabilities to identify and exploit vulnerabilities for malicious purposes.
PHP is estimated to power approximately 75% of websites and web applications worldwide.
Cloudflare, a provider of website infrastructure and cybersecurity services, said it had deployed protections against the vulnerabilities, collectively known as PHP2Shell, through its web application firewall (WAF).
The company said these measures were designed to block malicious requests targeting affected systems, providing an additional layer of defense while organizations update their software.
The PHP development team has released security patches.
Authorities have urged website operators to review the PHP versions running on their systems and apply the updates as soon as possible.
Node.js, LiteLLM and digital certificate systems also affected
The PHP vulnerabilities were far from the only cybersecurity challenge reported that day.
Node.js, the open-source JavaScript runtime environment, also announced an update addressing four critical security vulnerabilities.
One of the flaws could allow attackers to execute code remotely.
Two others could potentially bypass Transport Layer Security (TLS) authentication mechanisms, which are used to verify server identities and establish secure connections.
If exploited, these vulnerabilities could enable attackers to circumvent important security checks.
On the same day, LiteLLM, a popular open-source tool used to route requests to multiple large language model (LLM) providers, disclosed that hackers had compromised its software and inserted malicious code.
In a post on social media platform X on the afternoon of October 21, LiteLLM said malicious software packages and components had been distributed through PyPI, the Python Package Index, Docker Hub and GitHub Container Registry (GHCR).
The malware reportedly included information-stealing tools designed to capture cloud service credentials, passwords and login information for AI services.
It also contained a remote access trojan (RAT), potentially allowing attackers to execute commands on compromised systems.
LiteLLM said it had removed the malicious software releases and container images.
The company advised users who had installed affected versions to follow its remediation instructions.
Another incident involved eMudhra, an Indian digital certification service provider.
The organization's private key was compromised, raising concerns that attackers could issue fraudulent digital certificates and impersonate legitimate websites.
Security experts warned that addressing the consequences could be extremely complicated.
Some even suggested that the incident could exceed the scale of Heartbleed, the major security vulnerability previously discovered in the OpenSSL cryptographic software library.
Security teams face mounting pressure
The latest developments followed several other cybersecurity incidents reported in recent days.
Earlier in the week, the developer of the TiDB Cloud database service disclosed a security breach.
Meanwhile, hackers have been exploiting four previously patched vulnerabilities in Plex Media Server, collectively known as Plex2Shell.
Last week, cybersecurity company BeyondTrust also warned customers to urgently patch a critical zero-day vulnerability in its Remote Support product.
The flaw had reportedly been exploited since August.
Although the incidents are not directly connected, their rapid succession highlights the mounting pressure on cybersecurity teams worldwide.
The growing capabilities of artificial intelligence add another dimension to the challenge.
While AI can help security researchers discover vulnerabilities and develop defenses more efficiently, it could also enable attackers to identify and exploit weaknesses faster once they become known.
As a result, timely software updates, vulnerability management and incident response are becoming increasingly urgent for organizations operating internet-connected systems.
Du Lam

